Automation
SSL certificate monitoring with Python: verify what F5 and A10 actually serve
Check certificate expiry and trust at each VIP using the correct TLS hostname, then turn renewal warnings into actionable monitoring.
Read article
Technical notes and experiences from the field. On application delivery, security and open source.
Automation
Check certificate expiry and trust at each VIP using the correct TLS hostname, then turn renewal warnings into actionable monitoring.
Read articleAutomation
Authenticate safely, retrieve virtual-server configuration and close the session, with TLS verification and explicit error handling.
Read articleA10
Connect detection, traffic steering, mitigation and recovery in a DDoS design that measures the availability of legitimate services.
Read articleA10
Understand the ACOS object chain and the relationship between backend services, virtual ports, health checks and return-path design.
Read articleF5
Build a controlled HTTP redirect, preserve the request URI, choose the appropriate status code and investigate loops across the proxy chain.
Read articleF5
Compare monitor probes with application requests, inspect pool status and configuration, and investigate HTTP responses and network paths.
Read articleF5
Separate client-side and server-side TLS, test SNI and certificate trust, and locate the failing connection with OpenSSL and curl.
Read articleF5
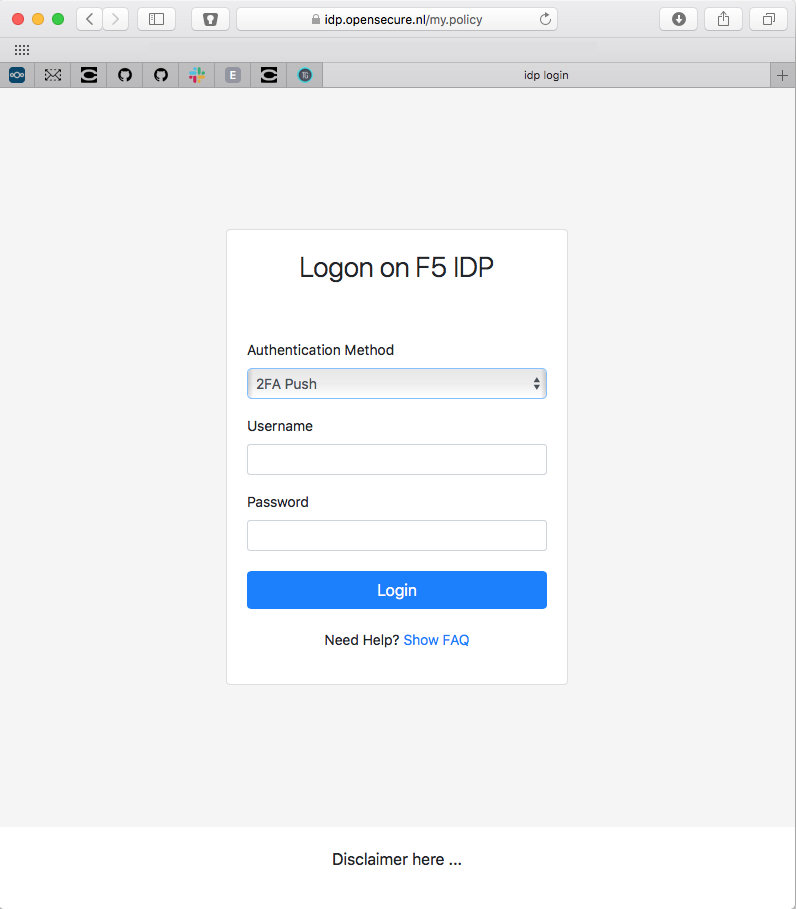
A custom F5 APM logon page with dynamic OTP and push authentication.
Read articleSecurity
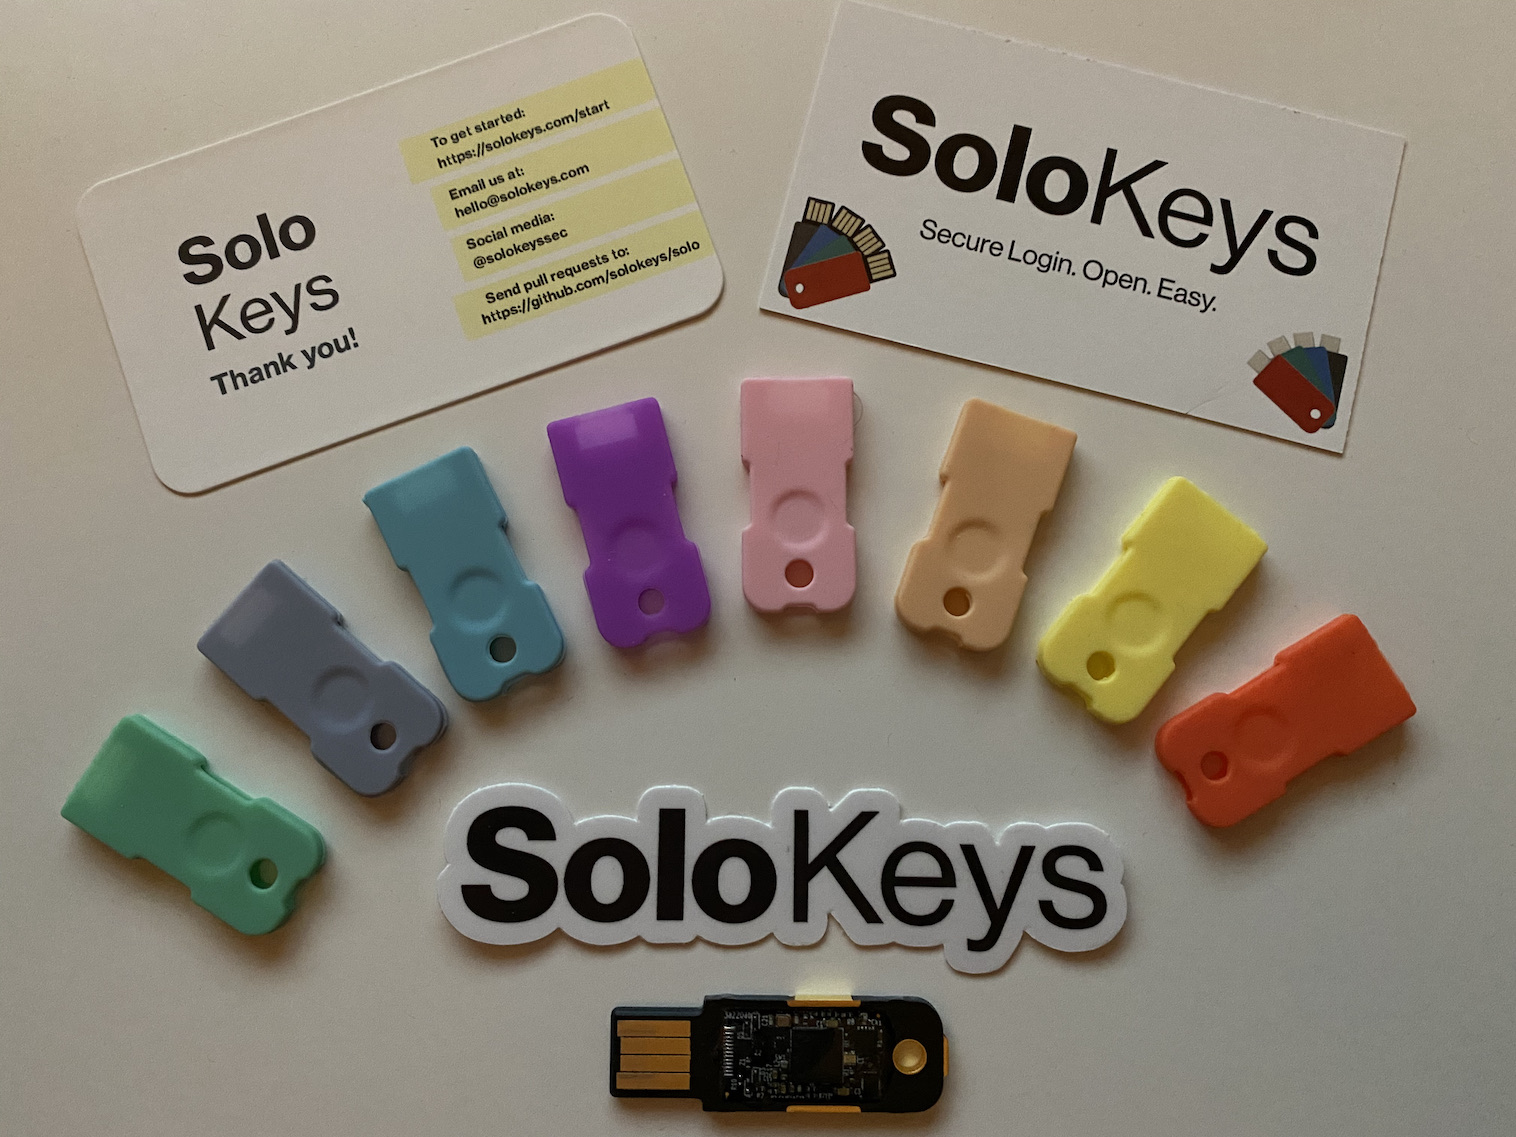
A look at the new hardware revision of the opensource FIDO2 security key.
Read articleBlocking spam and reducing mail-server load with Postscreen.
Read articleFirewall
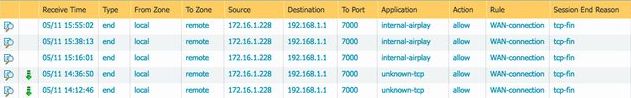
A closer look at the application field in Palo Alto traffic logs.
Read articleF5
Working with Data Guard in F5 ASM.
Read articleThere are no articles in this category.